California’s CCPA cybersecurity audits begin in 2027, with new requirements for covered businesses, annual audits, certifications, and reporting.
Continue Reading The Clock Is Ticking: Preparing for California’s First CCPA Cybersecurity Audits
California’s CCPA cybersecurity audits begin in 2027, with new requirements for covered businesses, annual audits, certifications, and reporting.
Continue Reading The Clock Is Ticking: Preparing for California’s First CCPA Cybersecurity Audits
The EU Cyber Resilience Act (CRA) makes cybersecurity a prerequisite for access to the EU market, not only for hardware products with digital elements, but also for software placed on the market independently. Its core requirements are far-reaching: conformity assessments, European Conformity (CE) marking, and a duty to supply security updates free of charge throughout
On Oct. 15, 2026, Greenberg Traurig Poland will host WHEN THE BREACH HITS: Legal and Business Leaders Cyber Incident Response Forum in Warsaw, bringing together senior legal, business, cybersecurity, risk, and crisis management professionals to explore the realities of responding to cyber incidents.
Designed as a highly practical program, the forum will examine real-world cyber
On Sept. 17, 2026, the California Lawyers Association Privacy + AI Lab will bring together legal and industry professionals to explore the rapidly evolving intersection of privacy, artificial intelligence, cybersecurity, and AI governance, with a focus on practical approaches to managing emerging legal and operational risks.
Greenberg Traurig Shareholder Gretchen Ramos, global co-chair of

In a May 6 webinar, GT Shareholders Jena M. Valdetero and Reena Bajowala will draw on lessons from thousands of real-world data breaches to help legal and business teams build stronger cyber incident response strategies. Register now.
Continue Reading May 6 WEBINAR | Cyber Incident Response: Lessons Learned From Thousands of Breaches
The amended Cybersecurity Law of China (CSL) entered into force on Jan. 1, 2026. These amendments, officially approved by China’s top legislature in October 2025, mark the first major changes to the law since it took effect in 2017.
Continue Reading China’s Amended Cybersecurity Law Takes Effect

Cybersecurity incidents pose a fundamental challenge: How do you reassure stakeholders while acknowledging that many facts remain unknown early in forensic investigations?
Continue Reading How to Reassure Stakeholders When Facts Are Still Unknown During Cyber Incidents
On Dec. 5, 2025, the German act implementing the EU NIS 2 Directive was published.
Continue Reading NIS2 in Germany: The New BSI Act Makes Cybersecurity a Board-Level Issue

The last remaining provisions of the amendments to the New York Department of Financial Services’ (DFS) cybersecurity regulation called Part 500 came into effect Nov. 1, 2025.
Continue Reading NYDFS Final Cybersecurity Rules – MFA, Asset Inventory, and Third-Party Risk
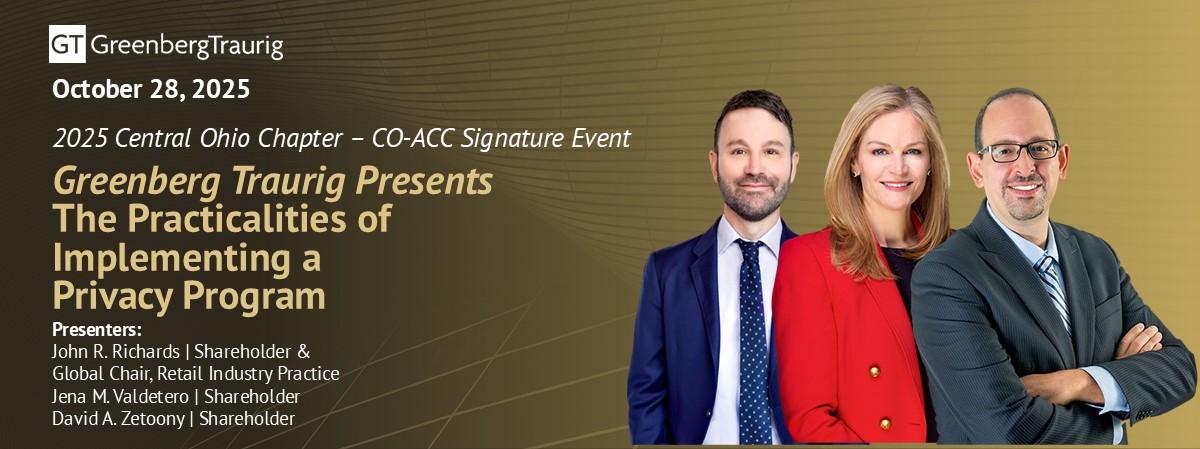
On Oct. 28, 2025, please join Greenberg Traurig and leaders from its Chambers USA Band 1 Retail Industry Group and Privacy & Cybersecurity Practice, along with a legal director from Scott’s Company LLC, for a CLE exploring the evolving landscape of data privacy and security laws and their impact on in-house legal teams.
This expert